Microsoft Azure · Sentinel · KQL
SIEM honeypot investigation
From authentication events to investigation and detection. Real query, login, and incident evidence.
Read the case studyStep-by-step walkthrough →The operations room
Investigations, identity workflows, and the decisions behind the work. Step into a case study to see the problem, the approach, and the evidence.
Featured investigation
★ The lab that got me the most interview questions
An Azure environment, failed sign ins, KQL investigation, and detection rules.
Open the case study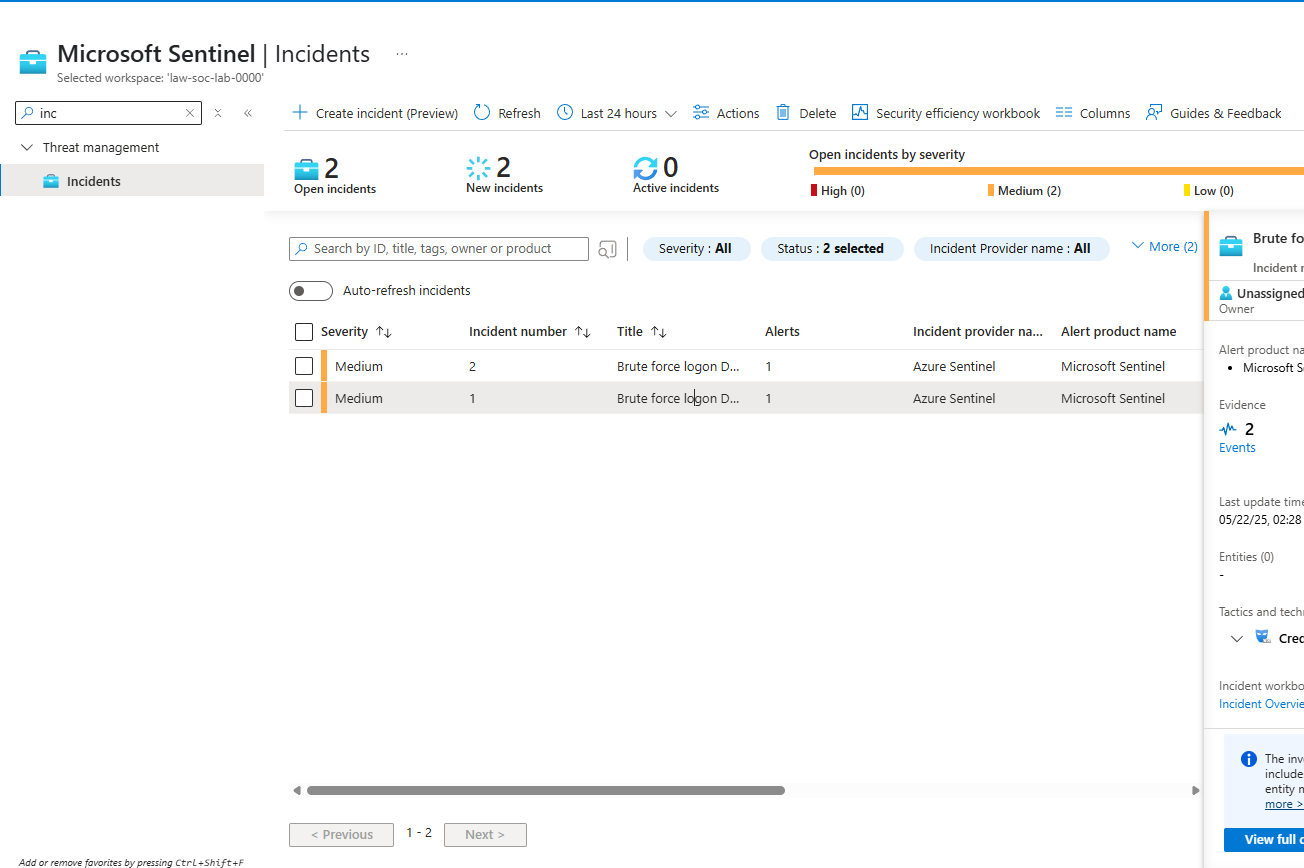 Explore the documented incident evidence
Building your own portfolio? It doesn’t have to be a thousand labs. Read my tips for a portfolio you can speak to →
Explore the work by focus.
Microsoft Azure · Sentinel · KQL
From authentication events to investigation and detection. Real query, login, and incident evidence.
Read the case studyStep-by-step walkthrough →Entra ID · Graph · PowerShell
Automating offboarding and validating the actions with the runbook output and workflow evidence.
Read the case studyStep-by-step walkthrough →Azure · Log Analytics
A documented foundation for centralized logging and security visibility.
Read the case studyStep-by-step walkthrough →NIST · Risk · Remediation
Connecting control gaps, business impact, and a practical remediation process.
Read the case studyStep-by-step walkthrough →